Implementation Model
Every use case in this section makes the same claim: verifiable trade is more scalable, higher integrity, and cheaper than the alternatives. This page explains the model that makes those claims hold.
The core idea
The authoritative sources of trust in trade already exist — national business registers, customs, intellectual-property and land registers. They have always been the authority. The only gap is that they have not made that trust digitally verifiable.
This model closes that gap with decentralised verifiable credentials (VCs) and DIDs, anchored on those existing national authorities. It does not insert a new intermediary, network, or platform between the trading parties — and that single choice is what makes it scale.
Centralised vs decentralised
| Centralised / intermediated | Decentralised (this model) | |
|---|---|---|
| Identity | A separate intermediary engages each business individually | The national register issues once; every registered business is covered |
| Documents | Routed through network hubs, reformatted, fee-metered | Issued peer-to-peer as VCs — no hub, no fee |
| Data security | Intermediary honeypots of sensitive commercial data | No intermediary store; identity from the source of truth |
| Recipient | Must be on the network (else fall back to PDF) | None — every document is human- and machine-readable |
| Domestic vs cross-border | Separate networks and builds | One architecture serves both |
| Adoption | Driven by legal mandate (high cost, low benefit) | Driven by real value, via systems of record |
How it works
- Identity comes from the authority, not an intermediary. One uplift of a national register makes verifiable identity available to all registered businesses — and can leverage national digital-identity systems that many economies already run. (See Identity Anchoring.)
- Documents are verifiable credentials, issued peer-to-peer. No routing hubs, no per-transaction fees, no intermediaries reformatting and storing the data. (See Portable Credentials.)
- Every document is both human- and machine-readable, so it works regardless of the recipient’s systems — there is no network-membership assumption.
- One architecture serves domestic and cross-border trade — every exporter also trades locally, so a single implementation covers both.
- Transferable records prove control, not just authenticity, through a standardised protocol rather than a proprietary platform — the key to scaling electronic bills of lading and similar instruments. (See Transferable Records.)
- Adoption is led by the systems of record — the accounting, ERP, carrier, and banking software businesses already use (optionally via business wallets) — not by a technology platform selling a single solution.
From declaration to evidence
The change this model makes to the relationship between a business and an authority is not primarily technical. It changes which party has to understand the rules.
Under the declaration model, an authority publishes the data elements it requires, and the work of satisfying them falls on the trader: read the regulation, establish which subset applies to this particular movement, map internal data onto it, assemble a declaration, and assert that it is correct. The authority receives assertions, and samples them to find out whether they hold. Every authority that publishes its own subset is another integration for the trader, which is how the European eFTI regulation arrives at 750 data elements across 202 subsets (see Semantic Layers).
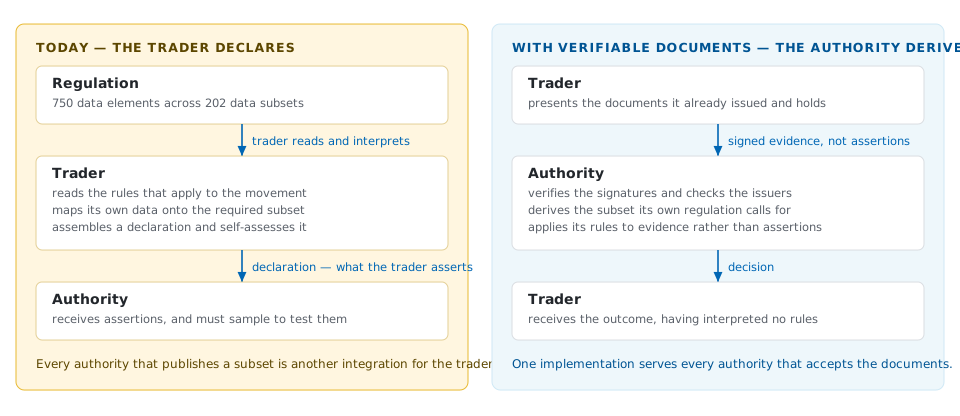
Under the evidence model the trader presents the documents it already issues and holds — the commercial invoice, the consignment note, the certificate of origin — as verifiable credentials. The authority verifies the signatures, checks the issuers against registers it already trusts, derives whatever subset its own regulation calls for, and returns a decision. The trader interprets no rules, because the party that wrote the rules is the party that applies them.
- The integration count collapses. A business that can issue its documents as credentials can satisfy any authority that accepts them, so one implementation replaces one per authority. The authority’s requirements can change without anything changing at the trader.
- The input improves. A declaration is a re-keyed summary asserted by the party with the most to gain from it. The underlying documents are signed by the parties that issued them — the carrier signed the consignment note, the chamber of commerce signed the certificate of origin — so the authority works from evidence instead of a claim about evidence.
- Controls stop depending on sampling. When documents arrive verified, checks that were affordable only on a small fraction of consignments can be applied to all of them (see Customs).
Where law requires a declaration, a declaration can still be produced. The difference is that it is derived from verified documents rather than asserted in advance of them.
Why it is better
- More scalable — because there is no shared network or platform that every party must join, the model works across dynamic, multi-party, multi-jurisdiction trades that defeat platform approaches.
- Higher integrity — identity from the source of truth, tamper-evident credentials, and cryptographically provable control mean fraud is detectable without trusting any intermediary.
- Cheaper to implement — a small, finite set of one-time uplifts (registers, systems of record, verifiers) replaces recurring network, transaction, and intermediary costs; marginal cost per business and per document approaches zero.
Learn more
The full rationale — including why the centralised identity-intermediary and network-hub (“4-corner / 5-corner”) models are the wrong choice — is set out in research/decentralised-model-case.md in the project repository. How the value and cost of this model are quantified is summarised in Assessment Methodology.